Webinar

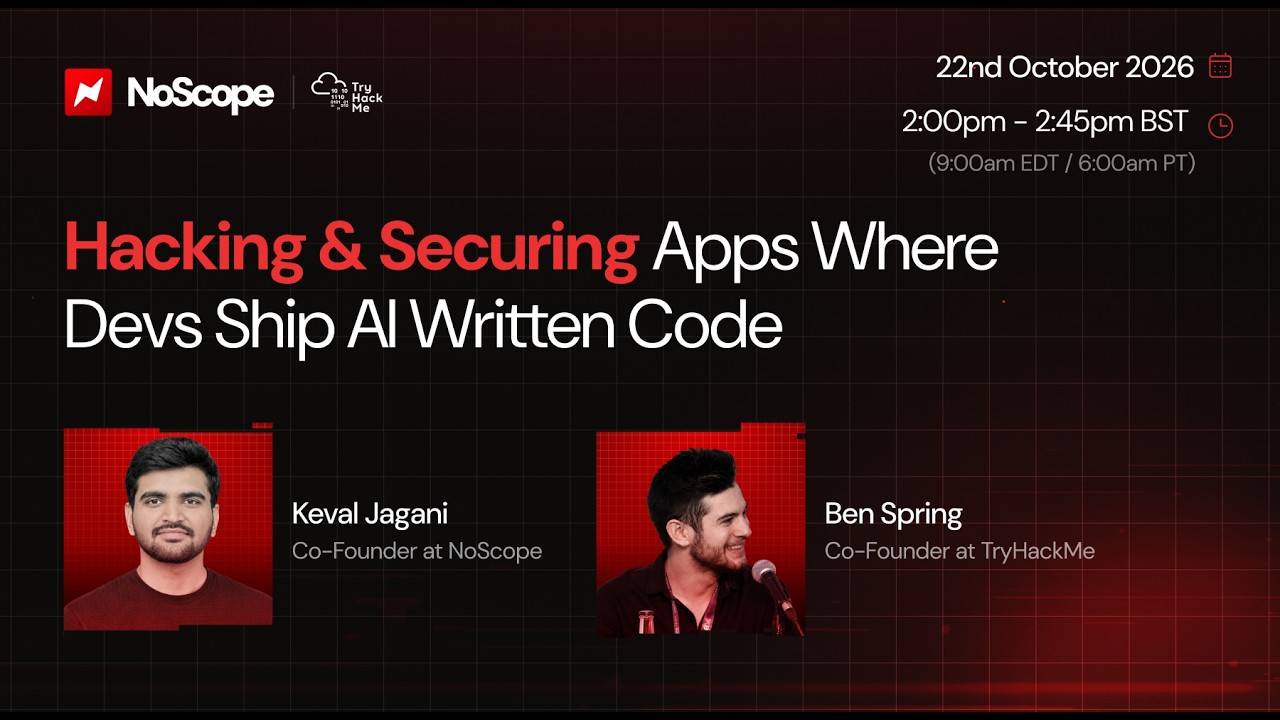
Hacking and Securing Apps Where Devs Ship AI Written Code

Webinar, hosted by Keval & Ben

Hacking and Securing Apps Where Devs Ship AI Written Code

This webinar covers the common vulnerabilities in applications written by AI and how to secure them.

What we cover:

  • How AI generated code scores in published security studies
  • The demo app, built with AI and left unfixed before testing
  • How NoScope turned 567 hypotheses into 57 confirmed findings
  • Customers reading other customers' tickets through a second API route
  • Login codes with no attempt limit and other missing controls
  • Hallucinated dependencies and how slopsquatting works
  • How Moltbook exposed its database through a Supabase misconfiguration
  • What to put in place to secure AI written code, and how to test it continuously
